Hightouch offers audit logs so workspace admins can see what actions users took in-app and when. For example, suppose someone notices that a sync has sent incorrect data to a destination. A workspace admin can use audit logs to review changes made to the sync before the incorrect data appeared. The admin can correct the issue, and—if necessary—implement controls to avoid future incidents.
View audit logs
Workspace admins can view logs by going to the Audit log tab on the Settings page. The logs consist of a table of actions beginning with the most recent. Each row represents one action.
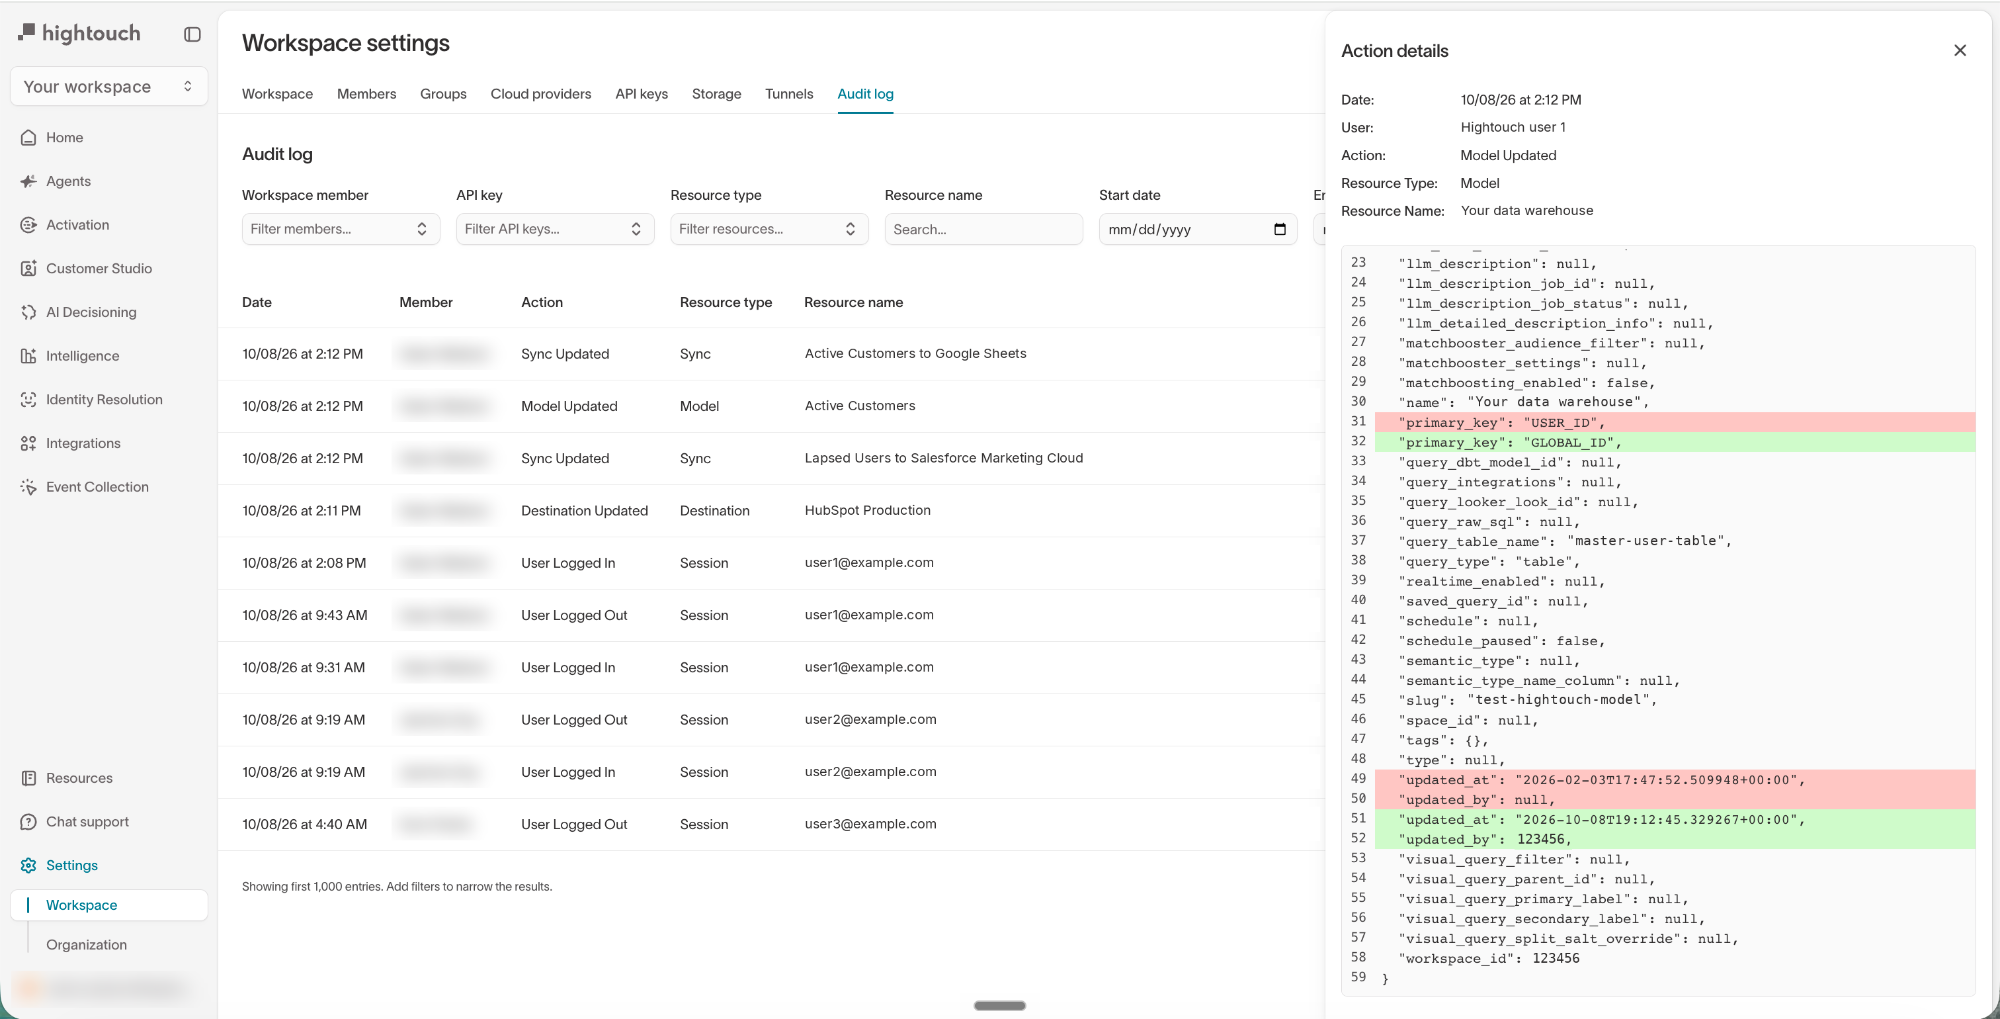
Each action includes:
- The Date and time, in the viewer's timezone, the action took place
- The Action name, for example, "Sync Updated"
- The Member who performed the action, with an API key badge if they made the change with an API key
- The Resource type of the resource the action was performed on
- The Resource name of the resource the action was performed on
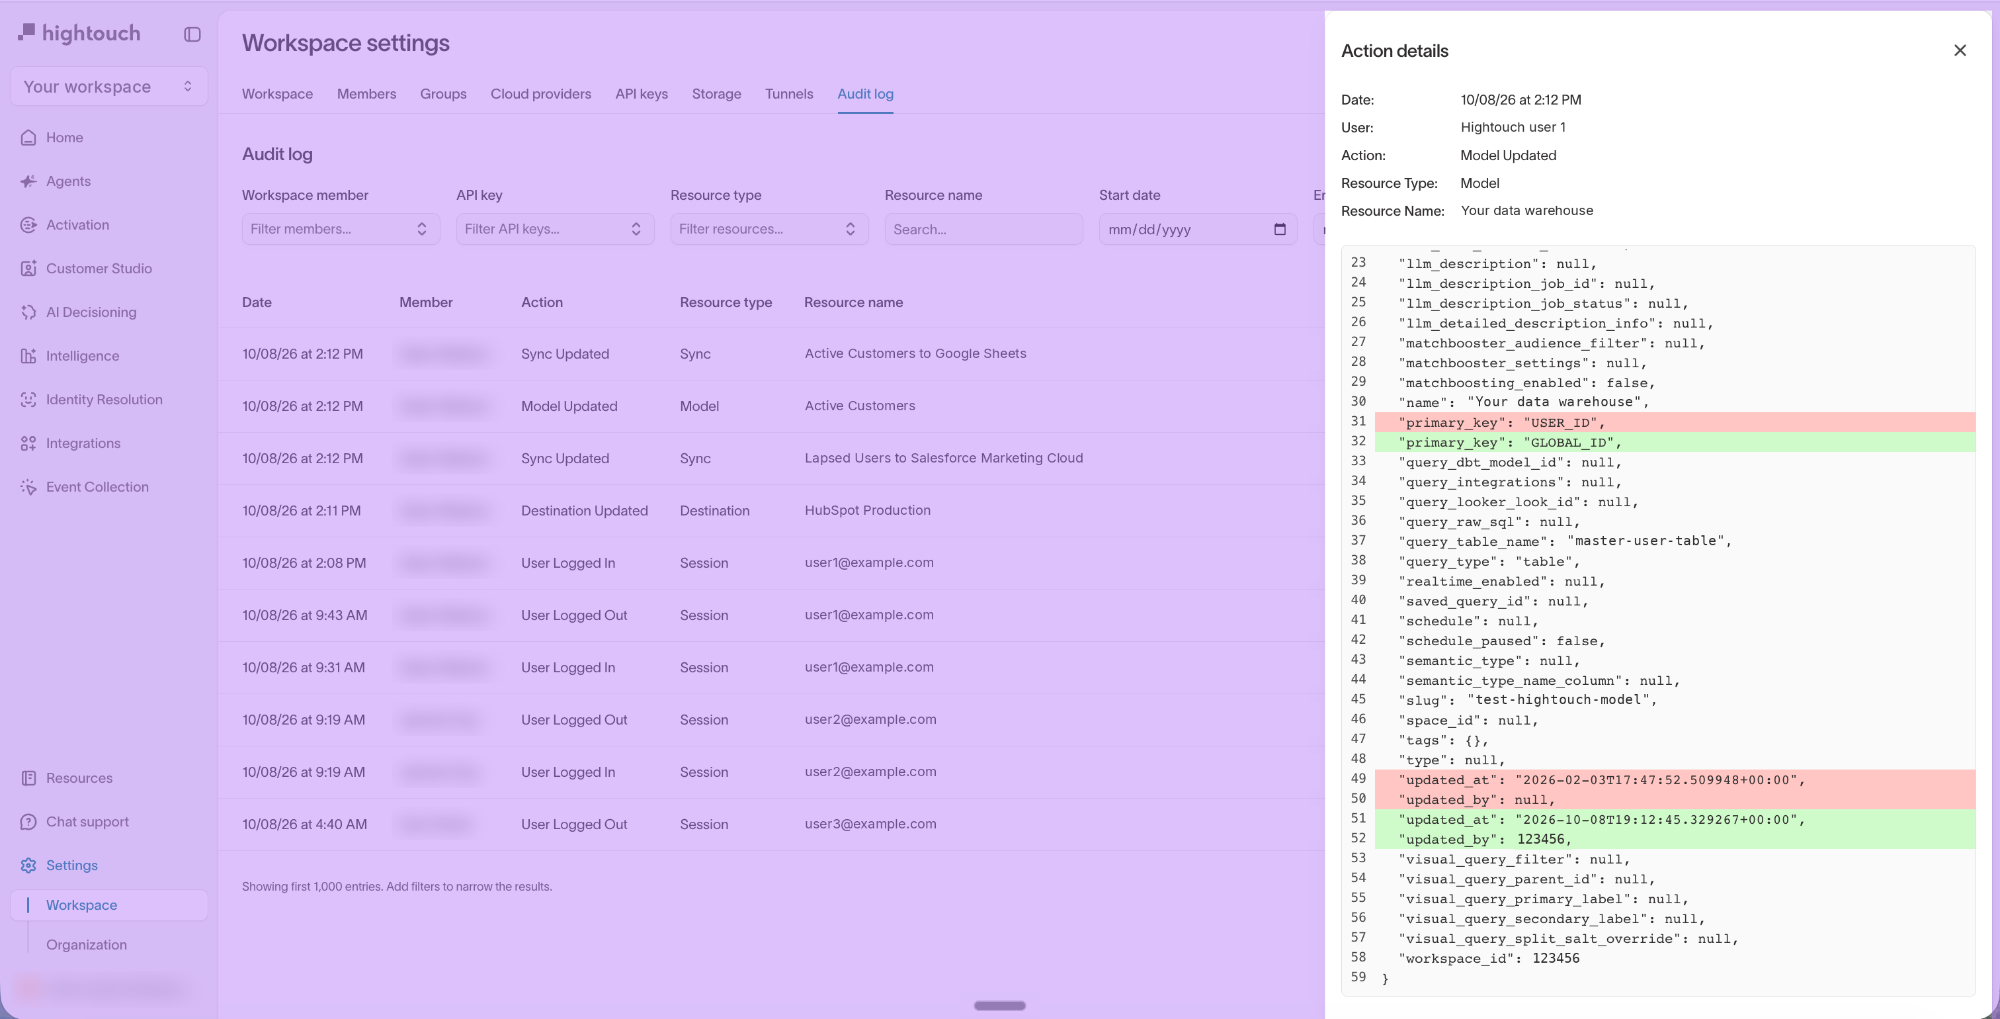
Clicking on an action opens its Action details panel, which shows the full change in JSON format. Added lines are highlighted in green, while removed lines are highlighted in red.
Filter audit logs
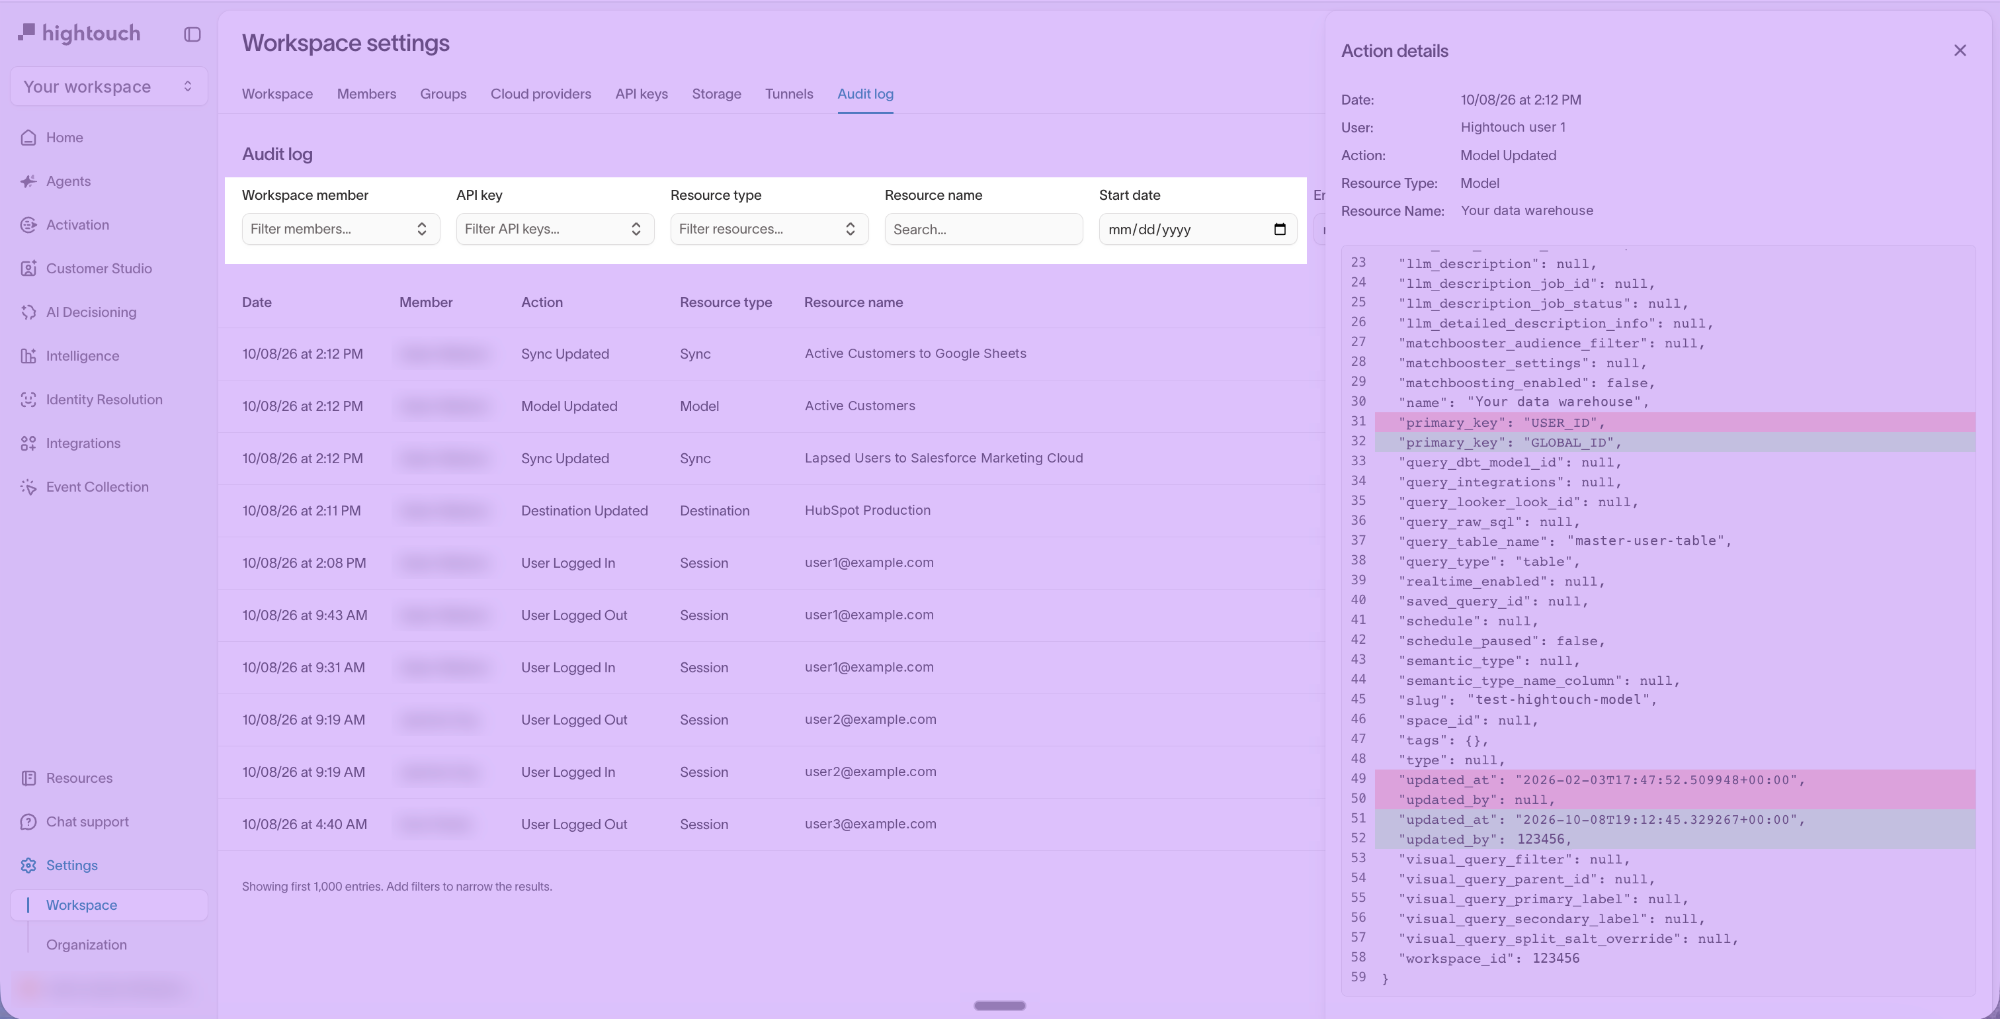
You can filter logs by:
- the workspace member who performed the action
- the API key used to perform the action
- the resource type the action was performed on
- the resource name the action was performed on
- a range of dates
You can select multiple members, API keys, and resource types to filter by simultaneously.
The table shows up to the first 1,000 matching entries. If you're looking for an older action, add filters to narrow the results.
Export audit logs
Workspace admins can export the audit log as a CSV file, for example to keep a copy for compliance reviews. The export includes the workspace's full audit log, not only the entries that match your current filters.
To export the audit log:
- Go to the Audit log tab on the Settings page.
- Click Export, then confirm.
Hightouch emails you a link to download the CSV file when the export finishes, which can take several minutes. The link expires after seven days.
FAQ
Who can view audit logs?
Users with the Workspace admin role in a workspace can view its full audit log. Organization admins receive this role automatically. Custom roles can't grant access to the full audit log.
Users without that role can still see the change history of an individual sync, model, or audience on its Activity tab, as long as they can view that resource.
What do audit logs include?
Audit logs track user-driven activity vs. programmatic changes. They work by taking a JSON snapshot of the changed resource for every user-driven change. Hightouch uses these snapshots for a before and after comparison for any changes.
A snapshot may include programmatic fields such as last_run_at, but Hightouch doesn't append a new audit log every time a field like last_run_at is updated since sync runs can be configured to run at regular intervals.
The exception to this is activity driven by Git Sync. For example, if a user changes a configuration via Git Sync, Hightouch treats that as a user-driven change, and it appears in the audit logs.
For a complete list of tracked actions, see the following list.
Resource types and tracked actions
Audit logs show creation, update, and deletion type actions for the following resource types:
| Resource type | Tracked actions |
|---|---|
| Alert | Creations, updates, or deletions of alerts you configure to inform you of syncing issues |
| Analytics query | Queries Hightouch runs against your source to calculate Intelligence charts and funnels, including the SQL it ran |
| API key | Creations and deletions of API keys Note: Audit logs record changes made with an API key, not every request that uses it |
| Approval request | Actions taken during approval flows, including sending a request to review a draft or approving a draft |
| Audience | Creations, updates, or deletions of audience configurations |
| Audience schema | Creations, updates, or deletions of parent models, relationships, and event models |
| Audience split | Creations, updates, or deletions of split groups in audience experiments |
| Audience template | Creations, updates, or deletions of audience templates |
| Cloud credential | Creations, updates, or deletions of cloud credentials, including changing your external storage configuration |
| Dashboard | Creations, updates, or deletions of dashboards |
| Dashboard chart | Creations, updates, or deletions of charts on a dashboard |
| Destination | Creations, updates, or deletions of destination configurations |
| Destination rule | Creations, updates, or deletions of destination rules |
| Draft | Creations, updates, or deletions of drafts used in approval flows |
| Event contract | Creations, updates, or deletions of event contracts |
| Event schema | Creations, updates, or deletions of the event schemas in an event contract |
| Git credential | Creations, updates, or deletions of Git credentials used for Git Sync |
| Git Sync configuration | Creations, updates, or deletions of Git Sync configurations; for example, changing your tracked Git branch |
| IDR | Creations, updates, or deletions of identity graphs in Identity Resolution |
| IDR golden record | Creations, updates, or deletions of an identity graph's Golden Record configuration |
| IDR model | Creations, updates, or deletions of the models an identity graph uses as inputs |
| Journey | Creations, updates, or deletions of journeys |
| Model | Creations, updates, or deletions of general model configurations, including updating the model query or primary key |
| Model column | Creations, updates, or deletions of model columns |
| Model preview | Actions taken while previewing a model, including a user clicking “Preview” while editing a model or running a SQL query against a source during model setup |
| Model trait definition | Creations, updates, or deletions of traits |
| Realtime audience sync | Creations, updates, or deletions of syncs for realtime audiences |
| Role | Creations, updates, or deletions of custom roles |
| Session | User sign-ins and sign-outs |
| Source | Creations, updates, or deletions of source configurations, including updating credentials or adding labels |
| SSO connection | Creations, updates, or deletions of SSO connections, including changing SAML settings |
| Subset | Creations, updates, or deletions of subsets |
| Subset audience assignment | Changes to which subsets an audience is assigned to |
| Subset category | Creations, updates, or deletions of subset categories |
| Subset category required model | Changes to whether a subset category is required for a parent model |
| Subset grant | Changes to which user groups can access a subset |
| Sync | Creations, updates, or deletions of sync configurations, including adding labels, scheduling, and turning a sync on or off |
| Sync run | Actions taken while viewing a sync; for example, a user clicking “Run” to start a manual run Note: Audit logs don't include scheduled sync runs nor API-triggered sync runs |
| Sync template | Creations, updates, or deletions of sync templates |
| User group membership | Additions and removals of users in user groups |
| Workspace | Workspace creation |
Older resource types
The Resource type filter also lists three types that Hightouch no longer records. They hold entries from before Hightouch moved workspace access to user groups:
- Invite — Workspace invitations. Invitations sent today are organization-level invitations, which workspace audit logs don't record.
- Membership — Workspace memberships. Adding or removing someone from a group now appears as User group membership.
- Membership request — Requests to join a workspace. Hightouch no longer supports these requests.
Changes not in the Resource type filter
Some changes appear in the audit log but aren't in the Resource type filter, so you can't filter for them by type. These include changes to which user groups can access the workspace, the roles and grants those groups have in it, and Identity Resolution graph runs. To find them, filter by member, resource name, or date range instead.